

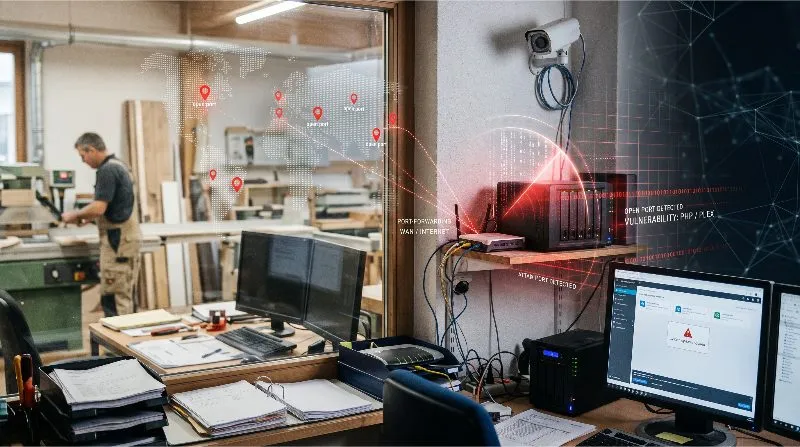
In its weekly review of 3 November 2026, the Swiss National Cyber Security Centre (NCSC, in German BACS) warns of a dangerous combination: devices with security vulnerabilities that can be reached from the internet. The NCSC received several reports of malware. The attackers got in through services that had been opened to the outside via port forwarding, and exploited vulnerabilities that nobody had patched.
The warning is aimed at private individuals. But anyone running a small office, a practice or a workshop should read it closely, because technically the network of many SMEs is nothing more than a larger home network.
What the NCSC describes
Port forwarding as a way in. To use a device while away, people make a single service reachable from outside through the router. That is convenient. But if the service is vulnerable, it sits directly on the internet.
Current vulnerabilities. The NCSC names the critical vulnerabilities in PHP, on which it published a separate warning on 21 October 2026, and flaws in the “Plex” media server. PHP often runs invisibly behind the web interfaces of devices and applications.
The consequences. According to the NCSC, they range from ransomware and extortion to data theft, covert crypto mining and abuse of the internet connection as a “residential proxy” that criminals use to hide where they are.
Hard to spot. “Those affected often only notice when they are being blackmailed,” the NCSC writes.
Why this matters to an SME
Look around a typical Central Swiss SME. There is a NAS with the project data that the boss also accesses from home. There is a security camera you can watch through an app. There is industry software with a web interface, a heating control, maybe an old remote maintenance access that a supplier set up years ago.
Each of these accesses was opened once for a good reason. And then forgotten. Automated scanners find open services like these in minutes, not weeks. They do not ask whether you are a large or a small company. They are just looking for the next hole.
Our view
Here is the sentence you rarely hear: port forwarding has no place in an SME network. Not for the NAS, not for the camera, not for remote desktop. Every open port is a bet that you patch faster than the attackers scan. Sooner or later, SMEs lose that bet.
The good news: the solution is neither expensive nor complicated. A VPN with a second factor replaces almost every port forward, and most current routers and firewalls can already do it. That is exactly what the NCSC recommends. You just have to set it up instead of taking the convenient route.
What you can do this month
Open the router and look. Have it show you the list of all port forwards. For each entry, ask: who needs it, for what, and does anyone even remember it? Whatever nobody can explain gets closed.
Move remote access to a VPN. Access to the NAS, cameras, internal applications and remote desktop runs only through a VPN, for example WireGuard or OpenVPN, protected with two-factor sign-in.
Update everything on the network. Not just PCs, but also the NAS, routers, cameras, printers and controllers. Check with your vendors whether the PHP updates from the NCSC warning have been installed.
Isolate whatever has to stay open. A service that genuinely has to be reachable from outside belongs in its own network segment (DMZ), with a password of at least 12 characters, a lockout after failed attempts and, where possible, access from Switzerland only.
Check supplier access. Ask every IT and maintenance partner which accesses they have into your network. Anything undocumented is blocked until it is documented.
One sign the NCSC mentions is worth knowing: a device slows down for no reason and its fan runs constantly. That can point to covert crypto mining. In that case the whole network needs checking, not just that one device.
If you would like support
We check with you which services on your network can be reached from the internet, close what is not needed and set up secure VPN access, on site in Central Switzerland or remotely.
More on this: Managed IT services and on-site support. Or call us: +41 41 511 21 11.
Sources: National Cyber Security Centre NCSC (BACS), “Woche 44: Wenn das Heimnetzwerk zum Einfallstor für Cyberkriminelle wird” (in German), 3 November 2026; NCSC, “Kritische Schwachstellen in PHP: Sicherheitsupdates sofort einspielen” (in German), 21 October 2026.


 Switzerland.